SRL Archive - News and General

We shoulda done this ages ago!


Sin

2012-08-25 01:02:39


eska

2012-08-25 01:04:22

[email]Marcus225@gmail.com[/email]
dolfin756
2132

Rate?

Vinyl Scratch

2012-08-25 01:09:02

^ 10!

I r pass security expert! I r rate u a 10!

grats

2012-08-25 01:09:36

legit as hell, but they don't allow you to type your pass :P

one of my passes (not saying which one) is i9t69uf4823^#%$0%$9fhasn1zx

all the others are similar B) , although not for rs cuz I don't play lol
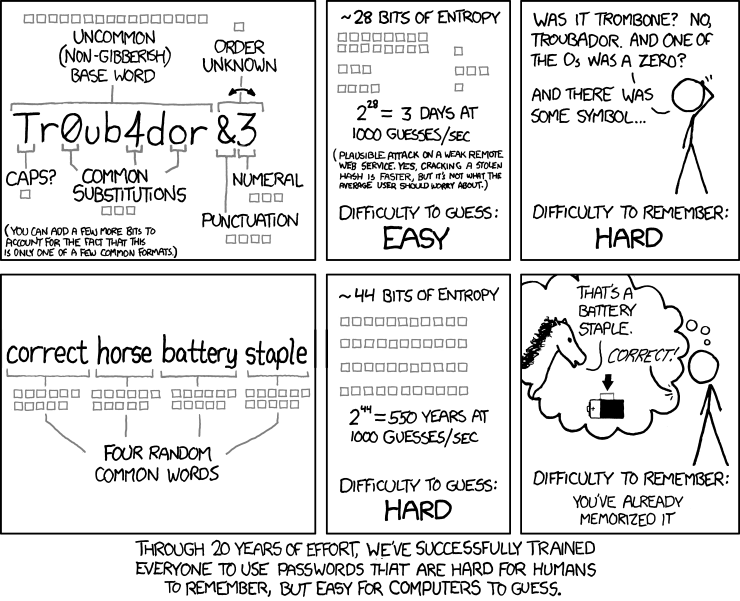
Vinyl Scratch

2012-08-25 01:11:32

^ No user, or bank pin. I hav to give u a 3.

grats

2012-08-25 01:13:18

^ not runescape, give your reading skillz 0

Sex

2012-08-25 01:16:29

From: grats
legit as hell, but they don't allow you to type your pass :P

one of my passes (not saying which one) is i9t69uf4823^#%$0%$9fhasn1zx

all the others are similar B) , although not for rs cuz I don't play lol


Better to use a phrase than random characters man.

grats

2012-08-25 01:20:48

From: Sex
Better to use a phrase than random characters man.


No.

Sex

2012-08-25 01:21:53

From: grats
No.


Why no?

grats

2012-08-25 01:25:04

From: Sex
Why no?


You're basing cracking off password character size

to guess an all text a-z A-Z it is like 4GB file, no problem at all..

my passwords are usually 200 characters, special characters, words, numbers, letters, caps, etc those take 100+GB files to crack along with a long ass time

and it's easy as shit for me to remember, I'm not some 90 year old who can barely remember 5 letter password

for example, some of my database user passwords are like:

76876%T&^%TR*&tG*67sar76d9fads6tR#$&%!T89Y(*FHG(USDT8ydtgas9-du7g-&(*t0ATGYSG)8d6ars6drdfw21g


Also, just to add, the main security threat is someone guessing a password, not someone brute forcing it.. brute forcing is pretty much dead. There's almost nothing that doesn't lock accounts out, lock IP's out, disable accounts.. after so many guesses etc.

Sex

2012-08-25 01:31:57

From: grats
You're basing cracking off password character size

to guess an all text a-z A-Z it is like 4GB file, no problem at all..

my passwords are usually 200 characters, special characters, words, numbers, letters, caps, etc those take 100+GB files to crack along with a long ass time

and it's easy as shit for me to remember, I'm not some 90 year old who can barely remember 5 letter password

for example, some of my database user passwords are like:

76876%T&^%TR*&tG*67sar76d9fads6tR#$&%!T89Y(*FHG(USDT8ydtgas9-du7g-&(*t0ATGYSG)8d6ars6drdfw21g


Also, just to add, the main security threat is someone guessing a password, not someone brute forcing it.. brute forcing is pretty much dead. There's almost nothing that doesn't lock accounts out, lock IP's out, disable accounts.. after so many guesses etc.

How the fuck is "76876%T&^%TR*&tG*67sar76d9fads6tR#$&%!T89Y(*FHG(USDT8ydtgas9du7g-&(*t0ATGYSG)8d6ars6drdfw21g" easy to remember?

Sin

2012-08-25 01:32:50

From: Sex
How the fuck is "76876%T&^%TR*&tG*67sar76d9fads6tR#$&%!T89Y(*FHG(USDT8ydtgas9du7g-&(*t0ATGYSG)8d6ars6drdfw21g" easy to remember?


Copy and paste :D

grats

2012-08-25 01:39:14

From: Sex
How the fuck is "76876%T&^%TR*&tG*67sar76d9fads6tR#$&%!T89Y(*FHG(USDT8ydtgas9du7g-&(*t0ATGYSG)8d6ars6drdfw21g" easy to remember?


Why would I remember a password that programs use?

find a keyboard style you like, and generate passwords with it

for example, keyboard opposites
q1 p0

those are opposite side of keyboard
lets make a password with those, while going inward and capitalizing every other letter and shift every number on every 3 skips:

q1p0W2O9e#i*R4U7t5y6

extremely easy to remember.
q1p0W2O9e#i*R4U7t5y6

not copied and pasted ^ typed in 10 seconds about

Sex

2012-08-25 01:40:32

From: grats
Why would I remember a password that programs use?

find a keyboard style you like, and generate passwords with it

for example, keyboard opposites
q1 p0

those are opposite side of keyboard
lets make a password with those, while going inward and capitalizing every other letter and shift every number on every 3 skips:

q1p0W2O9e#i*R4U7t5y6

extremely easy to remember.
q1p0W2O9e#i*R4U7t5y6

not copied and pasted ^ typed in 10 seconds about


Interesting. Meh.

grats

2012-08-25 01:41:56

I have some 20+ character passwords I can type in a few seconds, they're very random and make no sense looking at them but where your fingers move to is an extremely obvious pattern (once you know the password)

the example there is crappy & slow to type, however.. just find a fancy method maybe draw a square with each of your hands on the keyboard or something :P

Flight

2012-08-25 01:44:47

From: grats
Why would I remember a password that programs use?

find a keyboard style you like, and generate passwords with it

for example, keyboard opposites
q1 p0

those are opposite side of keyboard
lets make a password with those, while going inward and capitalizing every other letter and shift every number on every 3 skips:

q1p0W2O9e#i*R4U7t5y6

extremely easy to remember.
q1p0W2O9e#i*R4U7t5y6

not copied and pasted ^ typed in 10 seconds about


Haha genius.

grats

2012-08-25 01:46:35

That's how all my passwords are, don't find my secret drawing on the keyboard and hax0r me =[

riwu

2012-08-25 01:53:18

I've 5-9 digit passwords which can be typed in 1 sec (not kidding) and have never ever been hacked. The chance of guessing a password (username aside) within limits of getting locked is so slim that almost no one actually got hacked due to password being guessed. (mostly keyloggers etc)

grats

2012-08-25 01:59:10

From: riwu
I've 5-9 digit passwords which can be typed in 1 sec (not kidding) and have never ever been hacked. The chance of guessing a password (username aside) within limits of getting locked is so slim that almost no one actually got hacked due to password being guessed. (mostly keyloggers etc)


I agree, I always had short passwords till about 3-4 years ago I figured out designing stuff on the keyboard is a good way to make ridiculously overpowered passwords.. that are easy (for me at least) to type & remember

almost all accounts stolen are a form of keylogging, brute forcing is almost dead, in fact it's laughed at in hacking communities 99% of the time, some stuff is still able to get brute forced but it really isn't that great of a tool vs most

EtherFreak

2012-08-25 02:04:28

A password I use to use, props if you know why I used it. Guess I am turning into an old gezer

@red@BuyingRuneSets200k!

grats

2012-08-25 02:10:49

lol, I'm old enough to remember that spam if that's what you mean xD

Brandon

2012-08-25 02:29:50

From: grats
brute forcing is almost dead, in fact it's laughed at in hacking communities 99% of the time, some stuff is still able to get brute forced but it really isn't that great of a tool vs most


I beg to differ.. Brute forcing is never dead and never will die. No one I know laughs at it. Infact, it's still used to hack WEP and quite a bit of things.

That's like saying Lookup tables are dead. It's still a sorta brute force and it's used to reverse hashes and stuff. I personally still use John The Ripper and PattyCow for certain things.

If there is no sufficient exploit or algorithm, brute force/dictionary attacks are most likely the way to go.. So whoever looks down on it has a lot to learn. I think Crackers look down on it.. I doubt a hacker would.


INB4 Wizzup's Cracker vs. Hacker thingy ;)


EDIT: I refuse to make a new post..

@Grats:
You hack WEP with brute forcing? how terribly inefficient

Also I have yet to be on a private DNS / private IP / TOR hacking site where brute forcing isn't laughed at


I'd love to see you packet sniff Mixed-Mode WEP and successfully crack it without BruteForce. In case you don't know, those are the ridiculously expensive linksys routers that switch modes and sometimes broadcasting channels when too many packets are requested.

Also like I said. Anyone laughing at bruteforce or lookup tables is new to the game.

Flight

2012-08-25 02:36:31

From: EtherFreak
A password I use to use, props if you know why I used it. Guess I am turning into an old gezer

@red@BuyingRuneSets200k!


That's the old RSC text enhancer format. It was always the first 3 letters of the color, @ran@ was for rainbow, that was the most popular I think. :P

Oh man, I feel old…

grats

2012-08-25 02:41:38

From: Brandon
I beg to differ.. Brute forcing is never dead and never will die. No one I know laughs at it. Infact, it's still used to hack WEP and quite a bit of things.

That's like saying Lookup tables are dead. It's still a sorta brute force and it's used to reverse hashes and stuff. I personally still use John The Ripper and PattyCow for certain things.

If there is no sufficient exploit or algorithm, brute force/dictionary attacks are most likely the way to go.. So whoever looks down on it has a lot to learn. I think Crackers look down on it.. I doubt a hacker would.


INB4 Wizzup's Cracker vs. Hacker thingy ;)


You hack WEP with brute forcing? how terribly inefficient

Also I have yet to be on a private DNS / private IP / TOR hacking site where brute forcing isn't laughed at

Benny

2012-08-25 03:29:49

From: Flight
That's the old RSC text enhancer format. It was always the first 3 letters of the color, @ran@ was for rainbow, that was the most popular I think. :P

Oh man, I feel old…

This brought back memories too. I remember trying to find cheats for runescape and colours is what I found

litoris

2012-08-25 04:39:11

From: eska
[email]Marcus225@gmail.com[/email]
dolfin756
2132

Rate?


10/10, would hack again.

Leonardo Da Vinci

2012-08-25 05:13:25

From: grats
Why would I remember a password that programs use?

find a keyboard style you like, and generate passwords with it

for example, keyboard opposites
q1 p0

those are opposite side of keyboard
lets make a password with those, while going inward and capitalizing every other letter and shift every number on every 3 skips:

q1p0W2O9e#i*R4U7t5y6

extremely easy to remember.
q1p0W2O9e#i*R4U7t5y6

not copied and pasted ^ typed in 10 seconds about

That's brilliant.
I'm going to use methods like that for now on. Thanks!

Solar

2012-08-25 05:43:57

Nice method grats, but I can't be bothered with that.
OP; I'd like to know how many people he got before being banned. :p

Andres

2012-08-25 11:01:22

My passwords are all words I make up with random numbers and symbols thrown in. It's a similar system that grats uses. I make passwords that make sense phonetically but are nonsense to anyone other than me.

They're all really strong, I pmed that guy and he told me so.

Jos3ph

2012-08-25 11:38:32

HOLY shit did I just read that? DAMN!

stuartroad

2012-08-25 19:26:29

Hi, i have a completely no nonsense password, its also used as 90% of my passwords, I am yet to be hacked or keylogged yet.

Just sayin, I don't really believe you need all this algorithims or whatever the fk its called to have a safe password, just don't do dumb sheit

TehNeonFishy

2012-08-28 10:01:39

First laugh of the day. Wonder how many accounts he got :o

footballjds

2012-08-28 12:44:51

I use a phonetic password generator. It's the best fking thing ever!

Wyn

2012-08-28 14:54:11

From: Flight
That's the old RSC text enhancer format. It was always the first 3 letters of the color, @ran@ was for rainbow, that was the most popular I think. :P

Oh man, I feel old…


Tell me about it….