SRL Archive - Official Business

Change your passwords immediately!


Wizzup?

2011-09-09 11:28:29

Hey all.

I'm saddened to tell you that there has been a hack on villavu, similar to the one on MITB. (https://www.moparisthebest.com/smf/index.php/topic,514987.80.html). The attacker got in using the account of an admin (name doesn't matter), somehow also knew the password to the 2nd auth (HTTP auth, password may have been the same?) and got into the admin cp. Then changed the password of another admin that had access to the plugins section of VB, changed plugin code to something that resembles a minimalistic shell. I can only assume the worst and that he has indeed managed to dump (a part) of the database. The bandwidth logs would indicate something like this might have happened. The server itself seems to be safe - as the user only had access to the httpd account.

You must all fear for the worst. Check your PM's. If you ever sent a password over PM to anyone, make sure you change it. PM's are also part of the database. While this really sucks, in my defence I can only say there wasn't much to do to prevent this - social engineering and phishing just happens, I suppose.

This couldn't have come at a worse time as I am very busy trying to finish my bachelor thesis and I really don't have the time to install new forum software right now. However, it doesn't appear to be a problem with vBulletin - except for the idiots who work for them and decided you should be able to edit plugins (read: add php code) from the admincp.

It is very well possible the forum has been hacked due to an admin using the same password over at mopar's - or a previous forum that has been compromised. Let me say this just once more: Never, I repeat, NEVER use the same password across different sites.

Obviously we'll enforce a password change as well.
anonymity

2011-09-09 11:34:23

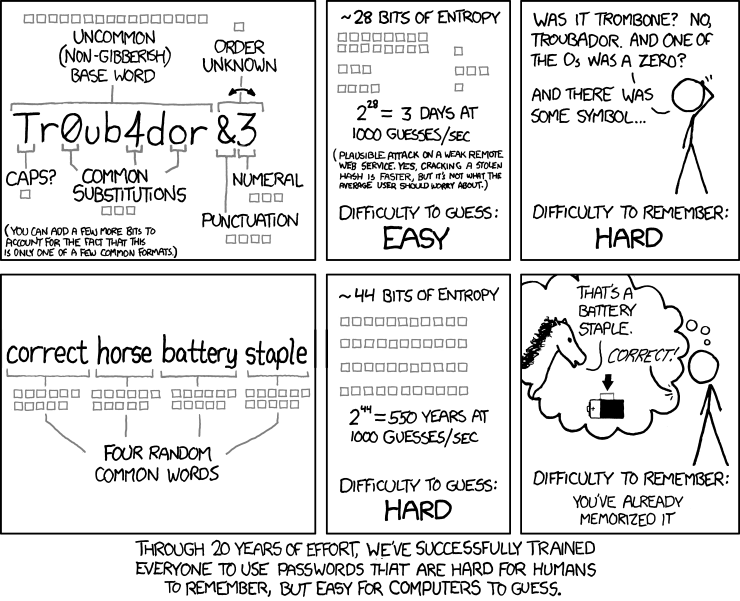
For people who might be having problems thinking of a new password, might I suggest :


Flight

2011-09-09 11:37:38

I wonder what they were trying to accomplish. My password is changed, now.

Wanted

2011-09-09 11:40:00

From: anonymity
For people who might be having problems thinking of a new password, might I suggest :


Password cracking rarely involves brute-forcing

Dictionary algorithms and common numbering patterns are also used.

anonymity

2011-09-09 11:43:40

From: Wanted
Password cracking rarely involves brute-forcing

Dictionary algorithms and common numbering patterns are also used.


Tis true; I usually l33t $p3@k phrases. Buuut, Ima go change a few passwords now…

footballjds

2011-09-09 11:44:38

From: Wanted
Password cracking rarely involves brute-forcing

Dictionary algorithms and common numbering patterns are also used.


correct

rainbow tables are used where they take the most common passwords. run 4012 iterations of a specific algorithm compile it into a huge "rainbow table" and then brute force them all.

for instance WPA2 security: (wiki)

If ASCII characters are used, the 256 bit key is calculated by applying the PBKDF2 key derivation function to the passphrase, using the SSID as the salt and 4096 iterations of HMAC-SHA1.[10]
the set of 95 permitted characters) is probably sufficient.[11] To further protect against intrusion, the network's SSID should not match any entry in the top 1000 SSIDs[12] as downloadable rainbow tables have been pre-generated for them and a multitude of common passwords.[13]

brute forcing has escalated from change a single letter at a time to just loading a big as table into memory and plowing through it… :(

Freddy1990

2011-09-09 11:55:47

Isn't it possible to force a password change with vBulletin?

Carlito

2011-09-09 11:57:21

how unfortunate :( hopefully this is the only that happens and we dont see a chain of events occur

Wizzup?

2011-09-09 11:59:32

From: Freddy1990
Isn't it possible to force a password change with vBulletin?


Yes and no. You can only set when passwords should expire. Most users should now be prompted if they have not changed their password in 30 days. (You should change your password regardless, this all happened about 4 days ago)

Kave

2011-09-09 12:16:03

I changed my password to the same until I saw this thread :o

litoris

2011-09-09 13:15:43

I was just prompted to change it upon login, said it expired. Good thing I use different passes for most sites. (passes made up of words of different languages that i can remember for most sites, real randomized stuff for important places that I could lose things at)

Dynamite

2011-09-09 13:50:01

From: Kave
I changed my password to the same until I saw this thread :o


This ^ :duh:

-Boom

onilika

2011-09-09 15:12:46

That's not good =/ Already changed my pass, but I think I will have to change it again, due to specific reasons. Is there any other way to prevent another attack to SRL community?

Wizzup?

2011-09-09 15:26:56

From: UNKNOWN69
That's not good =/ Already changed my pass, but I think I will have to change it again, due to specific reasons. Is there any other way to prevent another attack to SRL community?


Yes; don't use the same password on different sites. I've taken some more precautions but there isn't really a lot I could have done to prevent this. I'm sorry, for what it's worth. Let's hope this was the first and last time.

doom0791

2011-09-09 15:34:47

Hadn't realized my password was over three years old until I was told on login. Normally I'm better at changing my passwords than that :redface:, I guess SRL just managed to miss my regular change spree.

grats

2011-09-09 15:46:21

got prompted to change the pass so I did

weird they are trying to hack it =/ I have no similar passwords so all good


usually for my passwords I just smack my keyboard a few times and then memorize what comes out, use it as a pass.. got like 10 different ones

bevardis

2011-09-09 16:56:41

From: Flight
I wonder what they were trying to accomplish. My password is changed, now.


Get passwords and try them on mail or paypal

footballjds

2011-09-09 16:58:33

From: Wizzup?
Yes; don't use the same password on different sites. I've taken some more precautions but there isn't really a lot I could have done to prevent this. I'm sorry, for what it's worth. Let's hope this was the first and last time.


well, we know it wasn't the first…

weequ

2011-09-09 17:06:38

Ugh got to change my email password immediately. It was same as here :X

Echo_

2011-09-09 17:26:08

Interesting how they did this to both MITB and Villavu. I'm sure you and Moparisthebest will figure out who did this, it looks like the staff have narrowed it down to someone using a box in the Netherlands.

Harry

2011-09-09 18:37:53

It's obvious an inside job, or some admin who's really dumb, if you had the htaccess stuff on the admincp…

Yay for keepass, another random huge password to throw out.

Narcle

2011-09-09 21:04:10

heh… my last password was some random generated thing sent to my email… so no fear in them getting into anything else of mine. Changed mine already.

Wizzup?

2011-09-10 05:00:41

From: Harry
It's obvious an inside job, or some admin who's really dumb, if you had the htaccess stuff on the admincp…

Yay for keepass, another random huge password to throw out.


Don't forget a lot of people have (or now…had) access to the admincp. Old administrators and moderators, etc. About 15 I think. If you have someone else's HTTP auth (whatever we should call it), you can still get access to admincp using another admin user.

marpis

2011-09-10 08:23:47

I've used the same pw pretty much everywhere until now.
Ofcourse I've known that's bad, but I was just lazy and didn't bother changing it.
Now I came up with a whole new base word which I've never used before, and change the last letter in different sites, and I have the last letter for every site written down on paper.
:)

Harry

2011-09-10 09:00:14

From: marpis
Now I came up with a whole new base word which I've never used before, and change the last letter in different sites, and I have the last letter for every site written down on paper.

Cool, so if I figure out one of your sites I have a 3.84615385% chance to have your password from your other sites on my first guess.

Just get Keepass or something similar and use a long unique password that you will never forget, and use automatically generated ones per-site. :)

Jakkle

2011-09-10 10:53:03

I changed mine, left it as the random gen one and keep my self always logged in so I never have to type my pass in either.

vashanddou

2011-09-10 21:57:24

Speaking of passwords, anyone know a good free brute-force program? I forgot one of my passwords on a file that I encrypted its double encrypted and I forgot the first password =/ prob no more than 6-8 digits, second pass is 20+ digits which I remember lol.

Gu3st...

2011-09-10 22:13:49

@Wizzup?: So everyone who as access to admincp also has access to all of the forums users' passwords? Seems a bit odd to me :S

vashanddou

2011-09-10 22:33:33

From: vashanddou
Speaking of passwords, anyone know a good free brute-force program? I forgot one of my passwords on a file that I encrypted its double encrypted and I forgot the first password =/ prob no more than 6-8 digits, second pass is 20+ digits which I remember lol.


EDIT: because im only getting like 100p/s, 1k would be so much faster =/

Wizzup?

2011-09-11 06:41:50

From: Zyt3x
@Wizzup?: So everyone who as access to admincp also has access to all of the forums users' passwords? Seems a bit odd to me :S


No; it's not like that. They can CHANGE your password but not see or retrieve it. Unless they have access to the plugins which only I and Nielsie95 have. And Enigskai, an IRL mate and admin (because he's root on the server) had access to it. The cracker got in via one admin account (none of those) - found the HTTP auth for admincp in the PM inbox of this same admin. He then changed the password of Enigskai. (The admin was not protected from being modified - admins can change the password of other admins. Don't ask me why). Enigskai had access to the plugins which if basically PHP code. You can write a simple shell with phpBB code, and that's how he got access to the php files. Then you can read the mysql password for the user that owns the srl forums db. (And only the srl forums db). That's how he got the database. So, no. Admins don't have access to your passwords, and even still the passwords are salted and double md5'ed. (ugh, vBulletin again, but it's still somewhat protected if your password is not something like ``duck'')

How to prevent this? I'm going to make all the admin accounts non-modifyable. So you can't change a password, or even mail, signature - without asking me. And I can only hope everyone will use a more secure password and not the same one on other sites. And obviously HTTP auth passwords will not be in PM inboxes any more…

From: vashanddou
EDIT: because im only getting like 100p/s, 1k would be so much faster =/


Well, I know there is johntheripper, but I don't think it will fit your purposes. Unless you have the hash of the first password - and it doesn't sound like you have. May I suggest using something like EncFS ( http://www.arg0.net/encfs ) in the future?

Gu3st...

2011-09-11 07:27:48

From: Wizzup?
How to prevent this? I'm going to make all the admin accounts non-modifyable. So you can't change a password, or even mail, signature - without asking me. And I can only hope everyone will use a more secure password and not the same one on other sites. And obviously HTTP auth passwords will not be in PM inboxes any more…
Sounds good to me :)

bevardis

2011-09-11 07:47:03

From: Harry
Cool, so if I figure out one of your sites I have a 3.84615385% chance to have your password from your other sites on my first guess.

Just get Keepass or something similar and use a long unique password that you will never forget, and use automatically generated ones per-site. :)


This could be a problem when you reinstall your OSes from time to time;o

Harry

2011-09-11 07:59:37

From: bevardis
This could be a problem when you reinstall your OSes from time to time;o

No, you backup that pass vault…

masterBB

2011-09-11 15:16:56

From: Harry
No, you backup that pass vault…


Depending on if the system re-install was out of free will… :p Unless you meant like keeping it on a usb stick, that would be awesome. Also isn't it possible(if windows) to just search up the old pass vault in system.old …

vashanddou

2011-09-12 00:32:21

From: Wizzup?
No; it's not like that. They can CHANGE your password but not see or retrieve it. Unless they have access to the plugins which only I and Nielsie95 have. And Enigskai, an IRL mate and admin (because he's root on the server) had access to it. The cracker got in via one admin account (none of those) - found the HTTP auth for admincp in the PM inbox of this same admin. He then changed the password of Enigskai. (The admin was not protected from being modified - admins can change the password of other admins. Don't ask me why). Enigskai had access to the plugins which if basically PHP code. You can write a simple shell with phpBB code, and that's how he got access to the php files. Then you can read the mysql password for the user that owns the srl forums db. (And only the srl forums db). That's how he got the database. So, no. Admins don't have access to your passwords, and even still the passwords are salted and double md5'ed. (ugh, vBulletin again, but it's still somewhat protected if your password is not something like ``duck'')

How to prevent this? I'm going to make all the admin accounts non-modifyable. So you can't change a password, or even mail, signature - without asking me. And I can only hope everyone will use a more secure password and not the same one on other sites. And obviously HTTP auth passwords will not be in PM inboxes any more…


Well, I know there is johntheripper, but I don't think it will fit your purposes. Unless you have the hash of the first password - and it doesn't sound like you have. May I suggest using something like EncFS ( http://www.arg0.net/encfs ) in the future?


Well its some pretty important porn I gotta crack not gonna lie lol, so hopefully I remember the pass one day or find a good pass cracker for the first pass.

42069

2011-09-13 00:04:38

From: footballjds
correct

rainbow tables are used where they take the most common passwords. run 4012 iterations of a specific algorithm compile it into a huge "rainbow table" and then brute force them all.

for instance WPA2 security: (wiki)


brute forcing has escalated from change a single letter at a time to just loading a big as table into memory and plowing through it… :(


luv me sum rainbow hash